Palo Alto Networks: AI hunting vulnerability in legacy systems
Fri, 30th Oct 2026 (Today)
Palo Alto Networks is encouraging critical infrastructure operators to prepare for a convergence of information technology and operational technology, as AI accelerates the discovery of vulnerabilities in legacy systems.
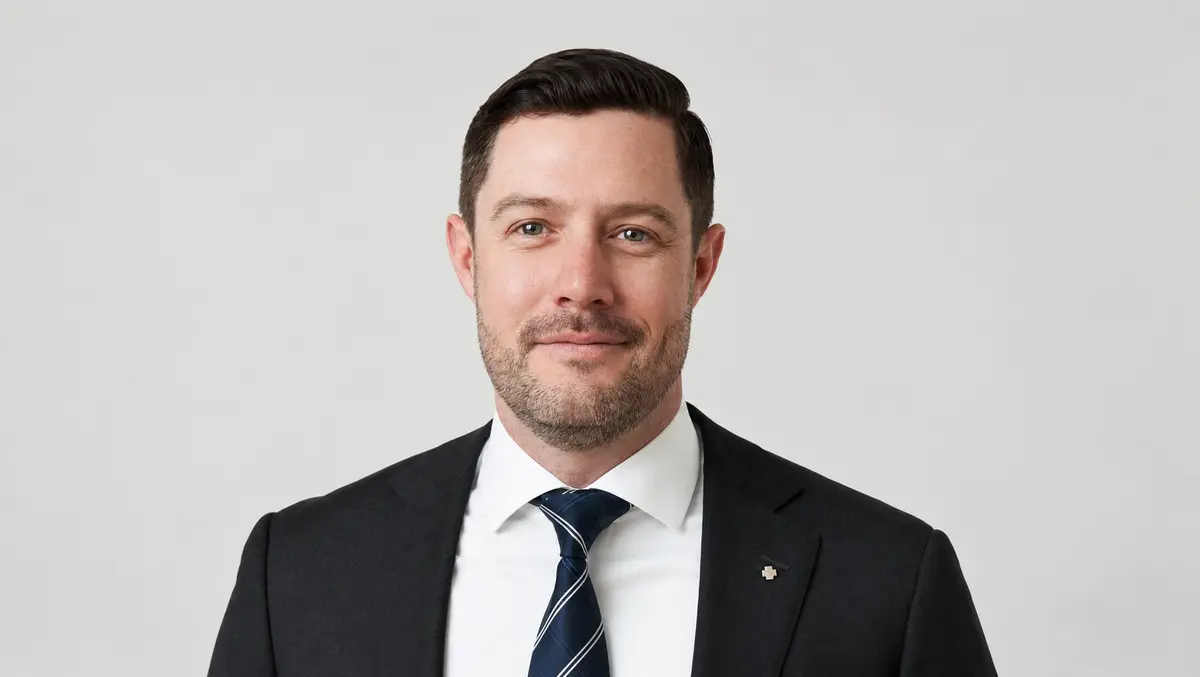
The increasing connectivity of industrial environments, combined with the adoption of AI-powered applications, is creating new cybersecurity challenges for organisations responsible for critical infrastructure, according to Tom Scully, Industry Principal, JAPAC at Palo Alto Networks.
Organisations must move beyond treating IT and OT as separate security domains, improving visibility across their environments and simplifying the tools used to detect and respond to threats.
"The importance of it coming together is the ability to get visibility over what is actually in your environment," Scully said.
"You can't protect what you can't see."
Speaking shortly after the release of Palo Alto Networks' 2026 State of Critical Infrastructure Cybersecurity Report, Scully said JAPAC respondents provided specific insights into the security concerns facing organisations in the region, with findings also reinforcing reflecting broader global critical infrastructure trends.
The report highlights the growing interconnectedness of IT and OT environments, which is bringing legacy industrial systems online and exposing them to vulnerabilities that were previously less accessible to external attackers.
AI accelerating cybersecurity challenge
AI is increasing the urgency of addressing these vulnerabilities, providing attackers with new ways to investigate targets, identify weaknesses and develop more convincing phishing campaigns.
Scully argued that cybersecurity teams must also adopt AI to improve their defensive capabilities, allowing them to respond to threats at a speed that would be difficult to achieve through manual processes alone.
"AI is incredibly useful for attackers, but on the other hand, it's also incredibly useful for defenders," he said.
"We have to be able to fight AI with AI in this new world."
However, companies still need to consider how AI could be integrated into existing security operations without adding further complexity.
Cybersecurity environments have accumulated specialised tools over time, with different departments adopting products to address individual security requirements. These can include tools for protecting internet-facing assets and monitoring industrial networks.
Organisations average seven tools within IT and OT environments, the report found.
Managing this fragmented environment creates additional work for security operations centres, which must recruit or train personnel to operate the tools, integrate them into existing systems and maintain them over time.
Consolidating security capabilities and bringing data together into a common layer would help organisations apply AI more effectively.
Reducing the number of separate systems could also lower the training and maintenance burden on security teams, while allowing them to respond to attacks more quickly.
Scully pointed to the potential for attackers to use AI across several stages of an operation, from open-source intelligence gathering to identifying potential entry points and developing targeted phishing campaigns.
Palo Alto Networks' JAPAC Industrial & Manufacturing Cyber-Risk Paradox report predicted that human-led defence models will be rendered mathematically obsolete by 2028, unable to defend against machine-speed attacks across dense 5G and IoT networks.
Security boundaries disappearing
Traditionally, OT networks have often been isolated from external networks through air-gapping.
This separation has helped protect industrial control systems by limiting their direct exposure to internet-connected environments.
However, the increasing operational and commercial benefits of greater connectivity are encouraging organisations to connect industrial systems more closely with IT infrastructure.
In manufacturing, as an example, connecting production environments can support greater efficiency, improve visibility across operations and help businesses implement just-in-time manufacturing and shipping.
The emergence of AI applications for industrial environments is expected to increase this connectivity further.
Industrial systems, including supervisory control and data acquisition (SCADA) platforms and programmable logic controllers (PLCs), could increasingly be used alongside AI-enabled applications for predictive maintenance.
Such applications could require industrial data to move beyond traditionally isolated environments so it can be processed by external or internet-connected AI workloads.
That creates a potential challenge, however, for organisations that have historically relied on separation between IT and OT to manage risk.
"It's inevitable these things will collide in the future," Scully said.
He encouraged organisational leaders to develop transition plans that consider how IT and OT environments will be connected, what risks that connectivity introduces, how those risks will be governed and which security tools will be required.
Scully said the challenge was particularly apparent for organisations operating multiple manufacturing sites.
Where each site is treated as an entirely separate environment, security personnel may need to access and assess each network individually before correlating findings across locations.
This can increase workloads and make it more difficult to maintain a comprehensive view of an organisation's security posture.
Improved visibility across industrial sites would help security teams identify vulnerabilities and understand how threats affecting one environment might relate to activity elsewhere.
Legacy systems could create long-term risk
Scully identified legacy technology as another major challenge for OT security in the near term.
Industrial systems can remain in operation for 10 to 20 years, and patching them can be difficult when equipment is located in remote sites or deeply embedded in operational processes.
The inability to update systems quickly leaves organisations exposed when vulnerabilities are discovered.
He warned that AI could accelerate the discovery of weaknesses in these older systems, increasing pressure on organisations to identify and mitigate vulnerabilities before attackers exploit them.
Virtual patching is one potential approach to addressing the problem.
Virtual patching involves applying protective measures that help block exploitation of a vulnerability without necessarily modifying the underlying system. This can be particularly useful where conventional patching is impractical or could disrupt industrial operations.
Palo Alto Networks has introduced frontier virtual patching capabilities in its PAN-OS 12.2 release, as a way to help address vulnerabilities in environments where systems cannot readily be updated.
Connectivity investments introduce new considerations
The increasing use of private 5G networks and satellite connectivity is also expected to affect the security of industrial environments.
Scully pointed to private 5G adoption as an increasingly prominent consideration for manufacturers seeking to connect industrial equipment and support applications that require greater bandwidth.
Existing wireless infrastructure may not be capable of carrying the volumes of data required by more advanced industrial applications, including those incorporating AI.
Upgrading connectivity could help address these limitations, but it would also create additional connections that organisations would need to secure.
Scully also highlighted the potential use of satellite services, including Starlink, to connect remote operational technology sites.
Satellite connectivity could provide an alternative to renewing expensive leased-line infrastructure used to connect remote facilities for companies operating in regional areas.
However, increasing the connectivity of previously isolated industrial assets could introduce new vulnerabilities and expand the potential attack surface.
Organisations should consider these changes as part of their broader IT and OT security planning, instead of treating connectivity upgrades as purely operational decisions.